
Business continuity and crisis management experts rarely talk about the gap between business continuity and IT disaster recovery planning.
But they should.
The distance between the IT disaster recovery program you have and what you need could be bigger than you think.
Like one of our clients whose IT disaster recovery plans for several critical systems needed to support a recovery time objective of 24 hours but were built for 7 days.
They’ve unknowingly been walking a tightrope over the Grand Canyon and hoping for the best. Because that 6-day gap could become a multi-million dollar problem in the face of a crisis.
My stomach is hovering somewhere above my head just thinking about it.
If you want to avoid canyon-sized gaps like this, and the potential consequences, your business continuity and IT disaster recovery functions need to work together closely.
But in most organizations, they aren’t working together at all.
Here, we explore the common reasons for this disconnect and what you can do about it. With our highly actionable tips, you’ll know how to make sure your disaster recovery program is planted firmly on solid ground. (For the full picture of IT DR itself, from strategy to testing, see our Ultimate Guide to IT Disaster Recovery.)
Could Gaps in Your IT Disaster Recovery Program Be Putting Your Organization at Risk?
Cyber threats proliferate and technology innovates at breakneck speed. Software and hardware must be continuously implemented and updated to keep pace. Yet business continuity programs are rarely responsive in providing the data, in both form and frequency, that IT needs to accurately plan its disaster recovery strategies.
Consequently, IT is often pressed to come up with its own answers to critical system requirements, such as availability, acceptable downtime or recovery time objectives (RTO), and recovery point objectives (RPO).
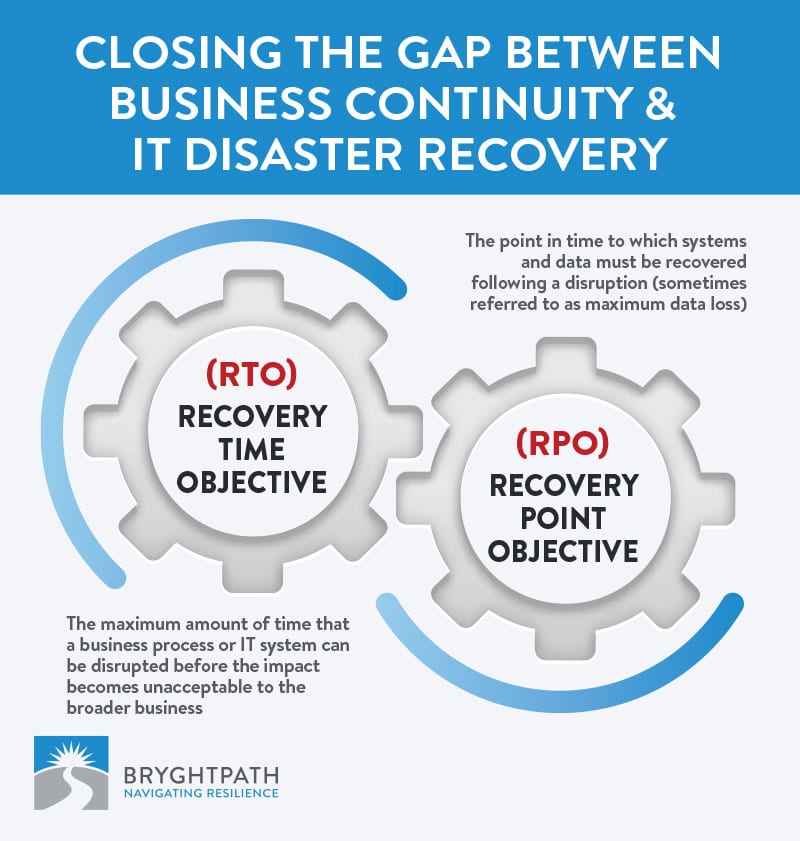
We think about Recovery Time Objective (RTO) as the maximum amount of time that a business process or IT system can be disrupted before the impact becomes unacceptable to the broader business. We think about Recovery Point Objective (RPO) as the point in time to which systems and data must be recovered following a disruption (sometimes referred to as maximum data loss).
But as the saying goes, “you don’t know what you don’t know.”
Business continuity and IT teams often assume they understand their IT disaster recovery requirements when they’ve actually got it all wrong. As a result, they architect inadequate solutions to their IT disaster recovery needs.
Your answers to the following questions will help you identify if your own organization could be at risk.
- Can you succinctly explain how your business continuity and technology or IT disaster recovery functions work together to ensure that critical technology applications are recovered to established RPO and RTO objectives?
- Can your teams clearly articulate the difference between business continuity, crisis management, and IT disaster recovery/IT technology continuity and also identify who is responsible for each function in your organization?
- Is your IT or disaster recovery team well represented on your business continuity and crisis management steering committee?
If you can’t confidently answer “yes” to all of these questions, you might have a problem.
- You can’t explain how your business continuity and technology or IT disaster recovery functions work together towards RPO and RTO objectives
- Your teams don’t understand the difference between business continuity, crisis management, and IT disaster recovery/IT technology continuity or know who is responsible
- Your IT or disaster recovery team is not represented on your business continuity and crisis management steering committee
Here’s how to get to solutions.
3 Ways to Close the Gap Between Business Continuity and IT Disaster Recovery
1. Make sure IT has a seat at the table
While IT should ideally own the disaster recovery process, their input is critical to both your organization’s overall technology strategy and in determining system availability and recovery requirements in the event of a disaster.
So the best and first way to close the gap between business continuity and IT disaster recovery is to ensure IT is represented in your business continuity and crisis management steering committee.
Working together with your steering committee, IT can help you more accurately and quickly assess:
- Where there are major gaps in your IT disaster recovery capabilities based on data from your business continuity program
- What needs to be done to close those gaps
- Which ones should be prioritized and which ones you may be willing to accept the risks based on your available resources and capabilities
At the outset, your conversations should also aim to get alignment on how you define business continuity, crisis management, and IT disaster recovery.
Over time, you should regularly revisit these discussions to address newly identified gaps between requested and actual recovery times.
2. Design your BIA process to capture the right data
Expecting your IT team to architect the right IT disaster recovery solutions without the right data is a lot like putting four wheels on a car but no gas tank and expecting it to drive.
Your business impact analysis (BIA) should be designed to capture the key data that your IT team needs to design an effective IT disaster recovery plan. That typically includes answering these two key questions:
- When does a specific business process need to be back up and running?
- What are its dependencies on third parties (vendors), technologies, facilities, and people?
Designing your BIA to answer these important questions will help your IT team better understand recoverability and availability requirements. As a result, they’ll be empowered to design more effective underlying applications and infrastructure recovery tiers. Cloud dependencies belong in that list too; we walked through why on Managing Uncertainty, Episode 314, after the October 2025 AWS outage.
3. Stick to the standards (ISO/IEC 27031, more precisely)
At Bryghtpath, we use the International Organization for Standardization (ISO) standards as the blueprint for our business continuity, crisis management, and disaster recovery planning efforts. Here’s why:
- ISO’s management system standards, including ISO 22301 for business continuity and ISO/IEC 27001 for information security, share the same high-level structure and core language. This aids the coordination of business continuity, crisis response, information security, and IT disaster recovery efforts across the organization and facilitates the clear communication of each respective function at the leadership level.
- ISO’s approach is largely based on the Plan-Do-Check-Act (PDCA) model. The PDCA model is a highly effective and proven approach for program improvement that ensures your program matures well over time.
ISO/IEC 27031, revised in 2025, is specifically focused on information and communication technology (ICT) readiness for business continuity. It helps you make sure your technology can deliver the recovery your business continuity requirements call for, and it covers testing and exercising that readiness, which should be a part of every IT DR program.
ISO/IEC 27031 is an excellent framework to help your IT DR program stay effective, align with industry standards, and grow to maturity over time.
Bryghtpath can help you step off the tightrope with confidence. Our IT disaster recovery consulting starts with the gap between what the business needs and what IT has built.
Keep Going
A few ways to go deeper if this was useful.
- Read more. The Ultimate Guide to IT Disaster Recovery and the Ultimate Guide to Business Continuity cover both sides of the gap.
- Get help on both sides. Our business continuity and IT disaster recovery services align your BIA, recovery objectives, and DR architecture.
- Get a maturity score. Our Resiliency Diagnosis® is a standards-based review, including ISO/IEC 27031, that produces a maturity score and a prioritized roadmap.
- Talk to us. Set up a call to find out how wide your gap is.