
Starting a business continuity program is not the same as writing a business continuity plan. A plan is a document. A business continuity program is the set of capabilities that keeps your critical work running when something breaks, and the discipline that makes those capabilities better every year.
Most organizations that call us to start a program already have a plan or two. What they don’t have is the structure around those plans: who owns them, what they’re based on, how anyone knows they work, and who in the C-suite cares. That structure is the program.
On the podcast, I laid out the 11 elements we look for in every business continuity program. You won’t have all 11 on day one. Nobody does. As I said in Managing Uncertainty, Episode 234, “we think of these 11 as kind of the essential building blocks of the areas of maturity for your program that you want to make sure that you’re growing towards over time.”
This post walks through the 11 elements, then the order we use to build them. For the full reference on the discipline, read our Ultimate Guide to Business Continuity. This is the practical companion: how to start.
What a Business Continuity Program Is Not
Sometimes the fastest way to define something is to say what it isn’t. A business continuity program is not:
- A business continuity plan, standing alone
- An IT disaster recovery plan
- A software subscription
- An insurance policy
- A template, a checklist, and a one-hour click-it-and-forget-it web training module
Each of those can be part of a program. None of them is the program.
| Old View | New View |
| Business continuity is a plan in a binder | Business continuity is a program with an owner, a budget, and a calendar |
| Build every element before you test anything | Build the essentials, exercise them, and grow toward the rest |
| Business continuity and IT disaster recovery run on separate tracks | One governance model, with recovery objectives set by the business |
| Participation is driven by compliance | Participation is driven by what the business needs to keep running |
| The program reports to the auditors | The program reports to your executives and the board |
The 11 Elements of a Business Continuity Program
1. Governance: policy and program management
Governance defines the scope, the objectives, and the management structure of the program. It includes a policy, standards, and standard operating procedures that say how your company commits to business continuity, who is responsible for what, and what resources the program gets. It also commits you to continual improvement and regular review.
In practice, governance means an executive sponsor with real authority and a steering committee that meets on a schedule. The governance section of our Ultimate Guide covers the policy, the sponsor, and the committee in detail.
2. Risk assessment
You need a process to identify the threats and vulnerabilities that could disrupt your operations, rated by likelihood and impact on your critical functions.
This one often lives somewhere else. “Often we see that this risk assessment doesn’t sit within a business continuity program and that’s okay. You just need to have one in your organization.” If your company has an enterprise risk management program, connect to it. Make sure the disruption risks it identifies are the ones your continuity work addresses.
3. Business impact analysis (BIA)
The business impact analysis is how you identify your critical functions and processes in a systematic way, decide how long each can be down before the impact becomes unacceptable, and set the order you recover them in. Call it maximum tolerable downtime or recovery time objective; the label matters less than the decision.
The BIA is the foundation for everything after it. Strategies and plans built without one are guesses.
4. Business continuity strategies
Strategies are how you keep each critical function going: alternative ways of doing the work, manual workarounds, relocating to an alternate site, remote work, or hot, warm, and cold recovery sites.
The pandemic changed this element more than any other. “Alternate workspace really has become less of a focus as it was, say, four or five years ago for business continuity.” The exception is hands-on work. If your people have to be physically present to do the job, alternate workspace is still a significant part of your strategy.
5. Plan development
Plans spell out what your teams do before, during, and after a disruption. Each plan should be tailored to the function it covers and include recovery objectives, clear roles and responsibilities, communication protocols, and response actions.
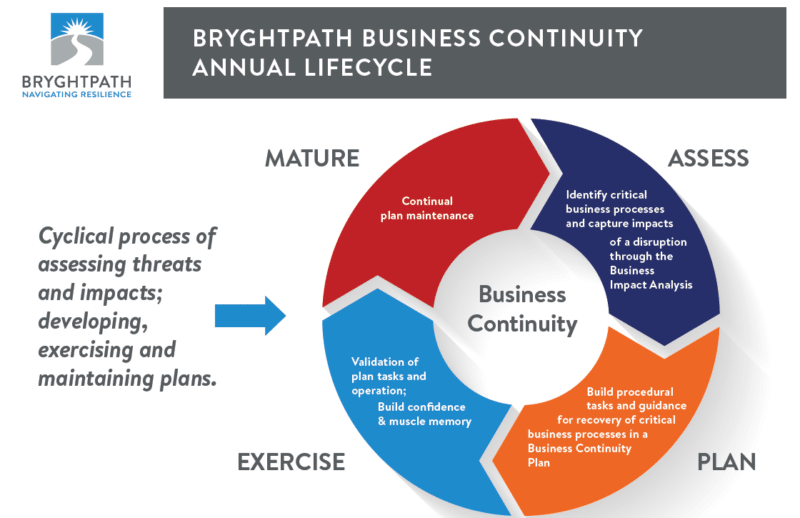
A plan is not a one-time deliverable. It is one stage of an annual lifecycle: assess, plan, exercise, and mature.
6. Training and awareness
Your people need to know why business continuity matters, what their role is in the plan, and what you expect them to do in a disruption. Training is ongoing, not a once-a-year event. Train plan owners before you exercise them; an exercise run with untrained people tests the training, not the plan.
7. Exercises
Exercises can run from a short discussion to several days. “The key though is that you wanna have exercises and capture lessons learned from those exercises on a regular basis.” Each exercise should end with an After-Action Report (AAR) that names an owner and a due date for every fix, and the next exercise should check that the fixes happened.
8. Program maintenance and review
Your business changes, so the program has to change with it: new risks, a reorganization, new technology, new regulations. Review the program on a schedule, through audits or strategic reviews.
That review has to reach the top. Report regularly to your C-suite and to your board, or at least to its audit, risk, or operations committee. As I put it on the show, “you need that strategic governance view to weigh in on your program and ensure it’s aligned with your organization’s strategic goals and objectives.”
9. Crisis communications
You need a plan for communicating with employees, customers, suppliers, and regulators during and after an incident. Your business continuity program may not own it. It might sit with crisis management, emergency management, or your marketing and communications team. “It might be wholly owned by your marketing or communications organization, but it has to be aligned,” with clear roles for who does what.
10. Coordination with external parties
Build the relationships before you need them: local police, fire, and EMS; local, county, state, and federal emergency management (or their equivalents outside the US); industry groups where information is shared; and your key third-party suppliers. With suppliers, the question is specific. How will they manage a disruption, how will you absorb its impact, and how will you communicate while it’s happening?
11. Alignment with IT disaster recovery
Business continuity and IT disaster recovery need “close coordination and, I would argue, common governance.” Your recovery time objectives and recovery point objectives should come from the business needs your BIA identified, not from what the infrastructure team guessed. That means knowing the hardware, software, data, connectivity, databases, and backups each critical function depends on. We wrote more about this in Closing the Gap Between Business Continuity and IT Disaster Recovery.
How to Start a Business Continuity Program
You don’t build all 11 elements at once. You build them in an order that protects your people first, then the work that keeps the business running. We use the same four steps for every program: Diagnose. Design. Deliver. Evolve.
Diagnose: know where you’re starting
Start with an honest baseline. What does your organization already have, formally or informally? Answer these before you write anything:
- Which strategic initiatives and critical functions does the program need to protect?
- How long can each critical function be disrupted before the impact is unacceptable?
- What do those functions depend on: technology, third parties, facilities, and people?
- How does your leadership actually collaborate and make decisions in a critical moment today?
- What plans already exist, who owns them, and when were they last exercised?
Most programs we evaluate start between 1.5 and 2.5 on a five-point maturity scale: informal, reactive, and scattered. That’s normal. What a business continuity maturity assessment should tell you explains how to get a baseline that means something.
Design: put governance in place first
Before you build plans, decide who owns the program. Name an executive sponsor, stand up a steering committee, and write a short policy that sets the scope and objectives. Then set the scope for your first year. Start with the functions that drive revenue, serve customers, or carry regulatory exposure. You can expand later.
This is also when you decide who does the work: an in-house team, an outside partner, or a mix.
Deliver: life safety, a crisis framework, then the first lifecycle
Build in this order:
- Emergency procedures. If a tornado hits or a shooter enters the building, your people need to know what to do in the first minutes: call 911, evacuate or shelter, and escalate. Give every location a short, accessible guide. Our Crisis Playbook® is built for exactly this.
- A crisis management framework. One way to escalate, decide, and communicate, used for every type of incident. Without one, departments write their own plans to fill the gap, and you end up with too many plans and no coordinated response. Add scenario annexes for your top risks once the framework is in place.
- Your first business continuity lifecycle. Run the BIA for the critical functions in scope, write their plans, train the plan owners, and exercise the plans.

A smaller organization may not be able to do all three at the same time. If that’s you, build the crisis management framework first, then phase in the business continuity lifecycle behind it.
Here is what that sequence looked like for one of the largest nonprofits in the United States, which retained us to build its first business continuity and crisis management program after an ad-hoc response to COVID-19. We started with a Resiliency Diagnosis® and a roadmap reviewed with its executives. Then we built an emergency procedures guide for each office and for remote workers, a crisis management framework and plan with five scenario-specific annexes and a tabletop exercise, and a full business continuity program. We ran its first lifecycle (BIA, planning, training, and exercises) and worked with its IT team to align business continuity and disaster recovery strategies.
Evolve: run it on a calendar
A program that only moves when someone has time doesn’t move. Put the year on a calendar and publish it. A simple version I described in Episode 229:
- First quarter: update program documentation.
- Second quarter: update existing plans.
- Third quarter: write new plans for organizational changes.
- Fourth quarter: exercise, and prepare for next year.
Once a year, review criticality across the organization, refresh the BIA, close the gaps your exercises found, and take a maturity score. Then report all of it to your executives.
Where New Programs Stall
After more than 30 years in this work, I see the same failure points again and again:
- Documenting everything before exercising anything. A year of plan writing with no exercise produces plans nobody has tested.
- A BIA nobody trusts. If the business doesn’t believe the recovery times, it won’t fund the strategies built on them.
- IT disaster recovery on its own track. The business expects four hours. IT can deliver four days. Nobody finds out until the outage.
- No executive sponsor. Without one, the program becomes a compliance exercise, and participation drops the moment the audit is over.
- Too many plans. Every department with its own crisis plan means no one knows which one is in charge.
None of these is a reason to wait. They’re a reason to start with governance and a baseline, not with templates.
A business continuity program is never finished. Start with an owner, your people, and your most critical work. Then build toward all 11.
Keep Going
A few ways to go deeper if this was useful.
- Read more. Resilience, crisis management, and continuity writing at Bryghtpath Insights, or the structured Ultimate Guide to Business Continuity.
- Build your program with us. Our Business Continuity services cover program design, BIA facilitation, plans, exercises, and IT disaster recovery alignment.
- Get a maturity score. Our Resiliency Diagnosis® is a standards-based review that produces a maturity score and a prioritized roadmap.
- Talk to us. Set up a call to think through your program with us.